Cloudflare · Security & Access
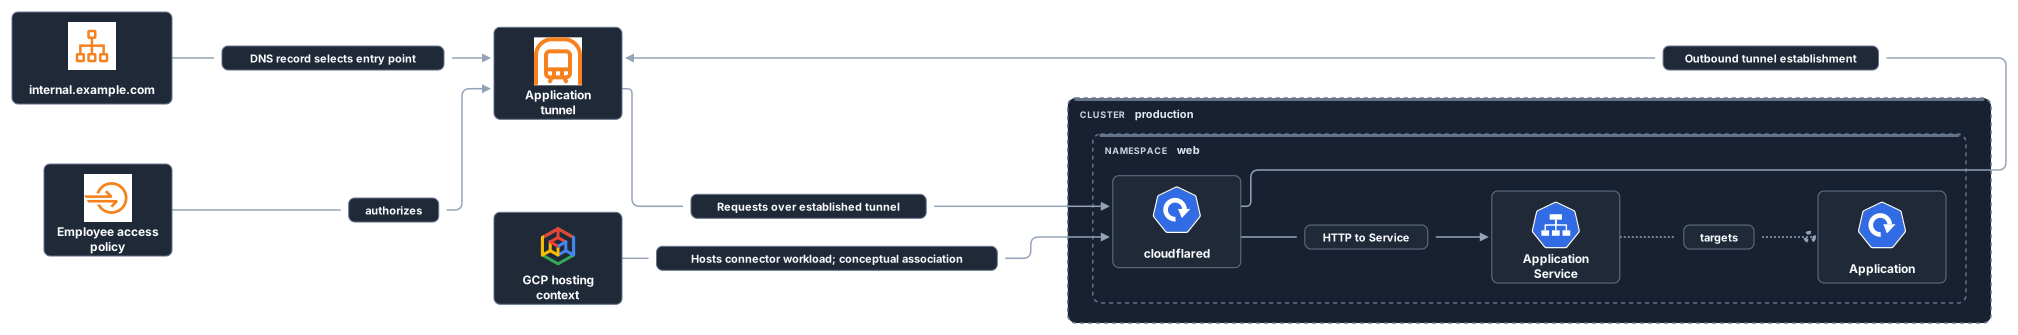
Access and a managed Tunnel connected to an origin-side cloudflared Deployment, with separate establishment and request flows. This diagram is written in ArchLex and passes Cloudflare provider checks.
provider cloudflare
direction LR
domain: cloudflare.dns["internal.example.com"]
access-policy: cloudflare.access["Employee access policy"]
tunnel: cloudflare.tunnel["Application tunnel"]
gke-host: gcp.gke["GCP hosting context"]
cluster production {
  namespace web {
    connector: k8s.deployment["cloudflared"]
    backend: k8s.service["Application Service"]
    application: k8s.deployment["Application"]
    connector -[proxies]->|HTTP to Service| backend
    backend -[targets]-> application
  }
}
domain ->|DNS record selects entry point| tunnel
access-policy -[authorizes]-> tunnel
connector -[connects]->|Outbound tunnel establishment| tunnel
tunnel -[proxies]->|Requests over established tunnel| connector
gke-host ->|Hosts connector workload; conceptual association| connectorSave the source as cloudflare-gcp-k8s-tunnel.arch and render it with the CLI, or ask your agent to adapt it through the ArchLex MCP server.
npx @archlex/cli render cloudflare-gcp-k8s-tunnel.arch --output cloudflare-gcp-k8s-tunnel.svg