Cloudflare · Networking
Cloudflare Public Edge to AWS
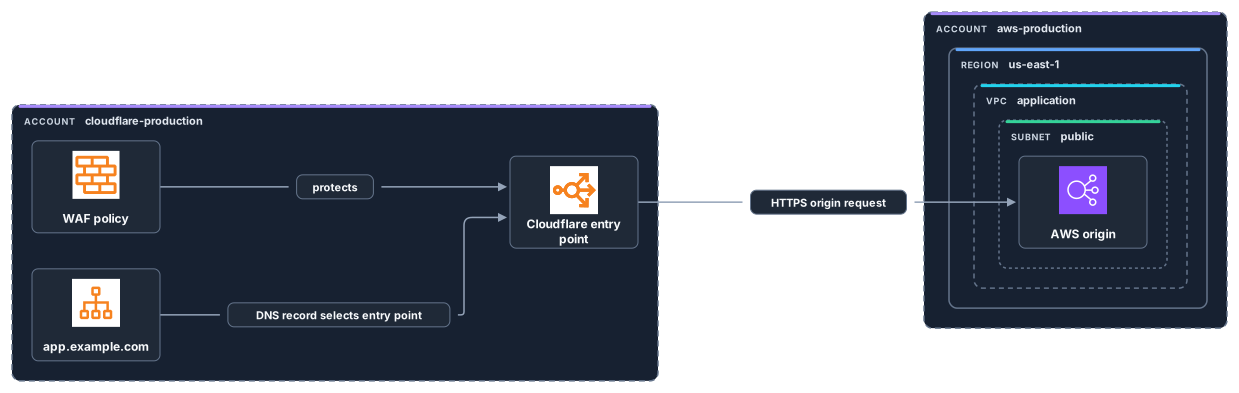
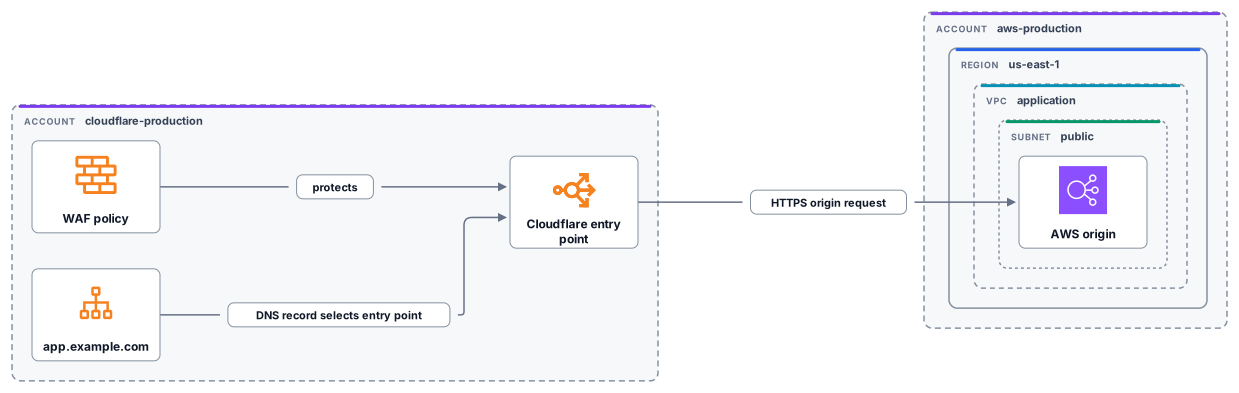
Cloudflare DNS, load balancing and WAF capabilities forwarding HTTPS requests to an AWS ALB. This diagram is written in ArchLex and passes Cloudflare provider checks.
Diagram and source
provider cloudflare
direction LR
account cloudflare-production {
domain: cloudflare.dns["app.example.com"]
entry: cloudflare.load-balancing["Cloudflare entry point"]
protection: cloudflare.waf["WAF policy"]
domain ->|DNS record selects entry point| entry
protection -[protects]-> entry
}
account aws-production {
region us-east-1 {
vpc application {
subnet public {
origin: aws.alb["AWS origin"]
}
}
}
}
entry -[proxies]->|HTTPS origin request| originWhat is in this diagram.
Resources
- app.example.com DNS
- Cloudflare entry point Load Balancing
- WAF policy WAF
- AWS origin Application Load Balancer
Relationships
- app.example.com connects Cloudflare entry point
- WAF policy protects Cloudflare entry point
- Cloudflare entry point proxies AWS origin
Boundaries
- account cloudflare-production
- account aws-production
- region us-east-1
- vpc application
- subnet public
Render it yourself.
Save the source as cloudflare-aws-public-edge.arch and render it with the CLI, or ask your agent to adapt it through the ArchLex MCP server.
npx @archlex/cli render cloudflare-aws-public-edge.arch --output cloudflare-aws-public-edge.svgRelated examples.
- VPC Subnet HierarchyProduction Account with us-east-1 Region, VPC, Subnet, and container database workload
- Secure Multi-Subnet VPC InfrastructureProduction Account with Public Subnet ALB/Security Group and isolated Private Subnets for ECS and RDS Database
- GCP VPC Network ArchitectureCloud Load Balancing routing to Compute Engine and Memorystore inside a regional VPC with subnets
- Cloudflare Workers & R2 ApplicationWorker entry point with DNS, WAF and response-cache capabilities, backed by R2