Kubernetes · Security & Access
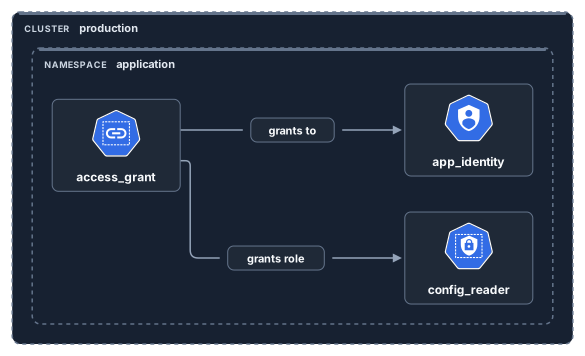
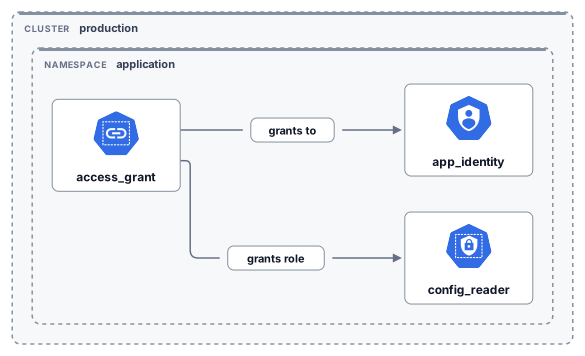
RoleBinding granting a namespaced Role to an application ServiceAccount. This diagram is written in ArchLex and passes Kubernetes provider checks.
provider k8s
direction LR
validation normal

cluster production {
  namespace application {
    app_identity: serviceaccount
    config_reader: role
    access_grant: rolebinding

    access_grant -[authorizes]->|grants role| config_reader
    access_grant -[authorizes]->|grants to| app_identity
  }
}Save the source as k8s-namespace-rbac.arch and render it with the CLI, or ask your agent to adapt it through the ArchLex MCP server.
npx @archlex/cli render k8s-namespace-rbac.arch --output k8s-namespace-rbac.svg