Cloudflare · Reliability & Scaling
Cloudflare AWS/GCP Origin Steering
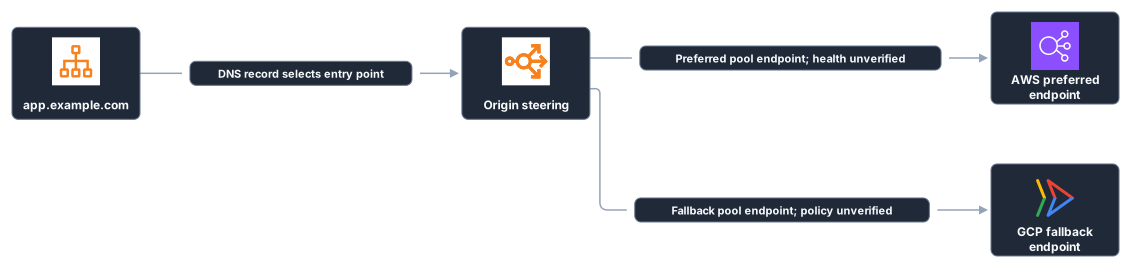
Preferred AWS and fallback GCP origin intent, without asserting verified health or steering policy. This diagram is written in ArchLex and passes Cloudflare provider checks.
Diagram and source
provider cloudflare
direction LR
domain: dns["app.example.com"]
steering: load-balancing["Origin steering"]
aws-origin: aws.alb["AWS preferred endpoint"]
gcp-origin: gcp.cloud-run["GCP fallback endpoint"]
domain ->|DNS record selects entry point| steering
steering -[routes]->|Preferred pool endpoint; health unverified| aws-origin
steering -[routes]->|Fallback pool endpoint; policy unverified| gcp-originWhat is in this diagram.
Resources
- app.example.com DNS
- Origin steering Load Balancing
- AWS preferred endpoint Application Load Balancer
- GCP fallback endpoint Cloud Run
Relationships
- app.example.com connects Origin steering
- Origin steering routes AWS preferred endpoint
- Origin steering routes GCP fallback endpoint
Render it yourself.
Save the source as cloudflare-aws-gcp-failover.arch and render it with the CLI, or ask your agent to adapt it through the ArchLex MCP server.
npx @archlex/cli render cloudflare-aws-gcp-failover.arch --output cloudflare-aws-gcp-failover.svgRelated examples.
- Multi-Region High Availability & DRCross-region active/passive failover with Route 53 DNS routing, primary and secondary VPCs, and database replication
- Kubernetes Autoscaled Resilient APIService and Deployment protected by horizontal autoscaling and a disruption budget
- Cloudflare Workers & R2 ApplicationWorker entry point with DNS, WAF and response-cache capabilities, backed by R2
- Cloudflare Public Edge to AWSCloudflare DNS, load balancing and WAF capabilities forwarding HTTPS requests to an AWS ALB